Introduction
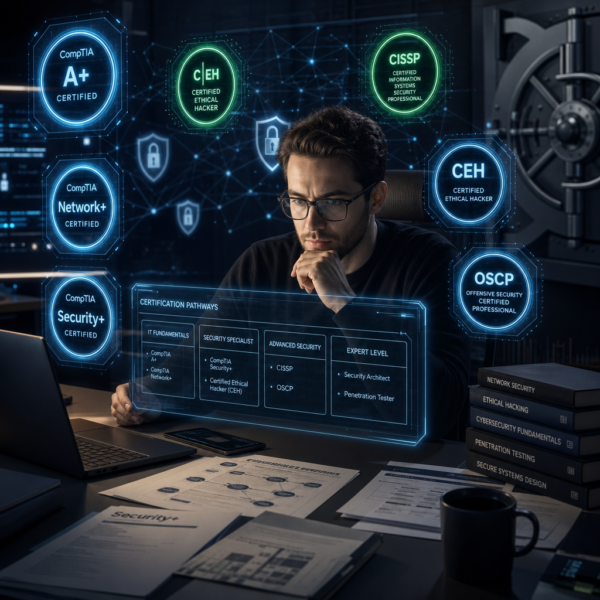
So you’ve decided to break into cybersecurity — great choice! The field is booming, job demand is sky-high, and today’s threat landscape is more dynamic than ever. But then comes the big question: which cybersecurity certification should I get first? With dozens of credentials floating around — CompTIA Security+, CEH, CISSP, and more — it’s easy to feel lost before you’ve even started. Don’t worry. This guide cuts through the noise and hands you a clear, friendly cert roadmap built for 2027’s job market.
Who This Guide Is For
This guide is for absolute beginners who are curious about cybersecurity but aren’t sure where to start. Maybe you’re a recent grad, a career-changer from a non-IT background, or someone who just binged a hacking documentary and thought, “I want to do that.” Whether you’re dreaming of joining a SOC (Security Operations Center) as a blue team analyst or eventually going red team as an ethical hacker, this guide will help you figure out your first move.
→ https://www.youtube.com/watch?v=hxA2OC_WDPk
Prerequisites / What You’ll Need
You don’t need a computer science degree to get started — seriously. That said, a basic comfort level with computers, networking concepts (think: what is an IP address, how does a firewall work), and operating systems like Windows or Linux will give you a solid head start. Some foundational IT knowledge — even a CompTIA A+ or Network+ cert — can be helpful, but it isn’t strictly required before you tackle your first security certification.
Step-by-Step Sections
Step 1: Start with CompTIA Security+
For most beginners, CompTIA Security+ is the undisputed first step. It’s vendor-neutral, widely recognized by employers, DoD-approved, and covers core concepts like threat detection, risk management, and cryptography. If you’re brand new to cybersecurity, Security+ is your smartest first move in 2027 — full stop. Once you’re ready to dive into prep, excellent courses are available across multiple platforms.
→ Explore top certifications for cybersecurity professionals
Step 2: Choose Your Specialization Path
After Security+, your path splits depending on what excites you. Interested in defending systems? The CompTIA CySA+ (Cybersecurity Analyst) is a natural fit for blue team work. Want to think like an attacker? The CEH (Certified Ethical Hacker) is a popular red team credential worth pursuing. For those eyeing management and architecture roles down the road, CISSP remains the gold standard — though it requires five years of experience first. Mapping out your cert roadmap early means you study with purpose rather than just collecting badges.
Step 3: Build Hands-On Skills Alongside Your Cert
Certifications open doors, but hands-on practice keeps you in the room. Set up a home lab, work through scenarios on platforms like TryHackMe or Hack The Box, and chase real-world context at every turn. Employers want to see theory and practice working together. Udemy’s massive cybersecurity library — taught by industry pros — pairs perfectly with cert study.
→ Top Cybersecurity Courses Online
Common Mistakes to Avoid
- Cert-collecting without context: Don’t chase every shiny credential. Pick a path and go deep.
- Skipping the basics: Jumping straight to advanced certs like CISSP without a solid foundation will hurt you in interviews.
- Ignoring soft skills: Communication, documentation, and problem-solving matter just as much as technical chops in SOC environments.
- Studying in isolation: Join communities on Reddit, Discord, or LinkedIn — the cybersecurity community is surprisingly welcoming.
Tools & Resources
- TryHackMe & Hack The Box — hands-on hacking labs for all skill levels
- Professor Messer’s free Security+ course — a perennial community favorite
- NIST Cybersecurity Framework — essential reading for understanding defensive frameworks
- CompTIA CertMaster — official practice exams straight from CompTIA
- Reddit communities like r/CompTIA and r/cybersecurity for candid, real-world advice
Next Steps
Passing your first certification is a milestone — but don’t stop there. Polish your LinkedIn profile, add the credential to your resume, and start applying for roles, even internships or junior SOC analyst positions. Entry-level jobs are genuinely available for Security+-certified candidates, and hiring managers notice the initiative.
From there, stack your certs strategically based on the role you want and keep your skills sharp with continuous learning. Cybersecurity rewards the curious and the persistent — so keep going.
FAQ
Q: Is CompTIA Security+ enough to get a job? A: For many entry-level roles — especially SOC Tier 1 analyst positions — yes! Pair it with hands-on experience and you’re in great shape.
Q: How long does it take to get Security+? A: Most people study for 1–3 months, depending on their background and daily study time.
Q: Do I need a degree to get certified? A: Nope. Certifications are often valued more than degrees in cybersecurity hiring.
→ https://www.youtube.com/watch?v=hxA2OC_WDPk
Q: What’s the difference between red team and blue team? A: Red team = offensive (ethical hacking, pen testing). Blue team = defensive (monitoring, incident response, SOC work).
Q: Is CISSP worth it for beginners? A: Not yet — CISSP requires five years of experience. Treat it as a mid-to-senior career goal.
Also worth reading:
Career Change to Cybersecurity in 2026: Certs, SOC Roles & Salary Roadmap
CompTIA Security+ vs Google Cybersecurity Certificate: Which Should You Take First?
Cybersecurity Without a Degree: 2026 Career Roadmap (Certs, Salaries & SOC Jobs)
Sources
- https://www.youtube.com/watch?v=hxA2OC_WDPk
- https://www.reddit.com/r/CompTIA/comments/1e6cy94/which_entrylevel_certification_for_cybersecurity/
- https://www.infosecurityeurope.com/en-gb/blog/guides-checklists/top-10-cybsersecurity-certifications.html
- https://counseltrain.com/top-10-cybersecurity-certifications-in-2027-ranked-counseltrain-technology-dubai/